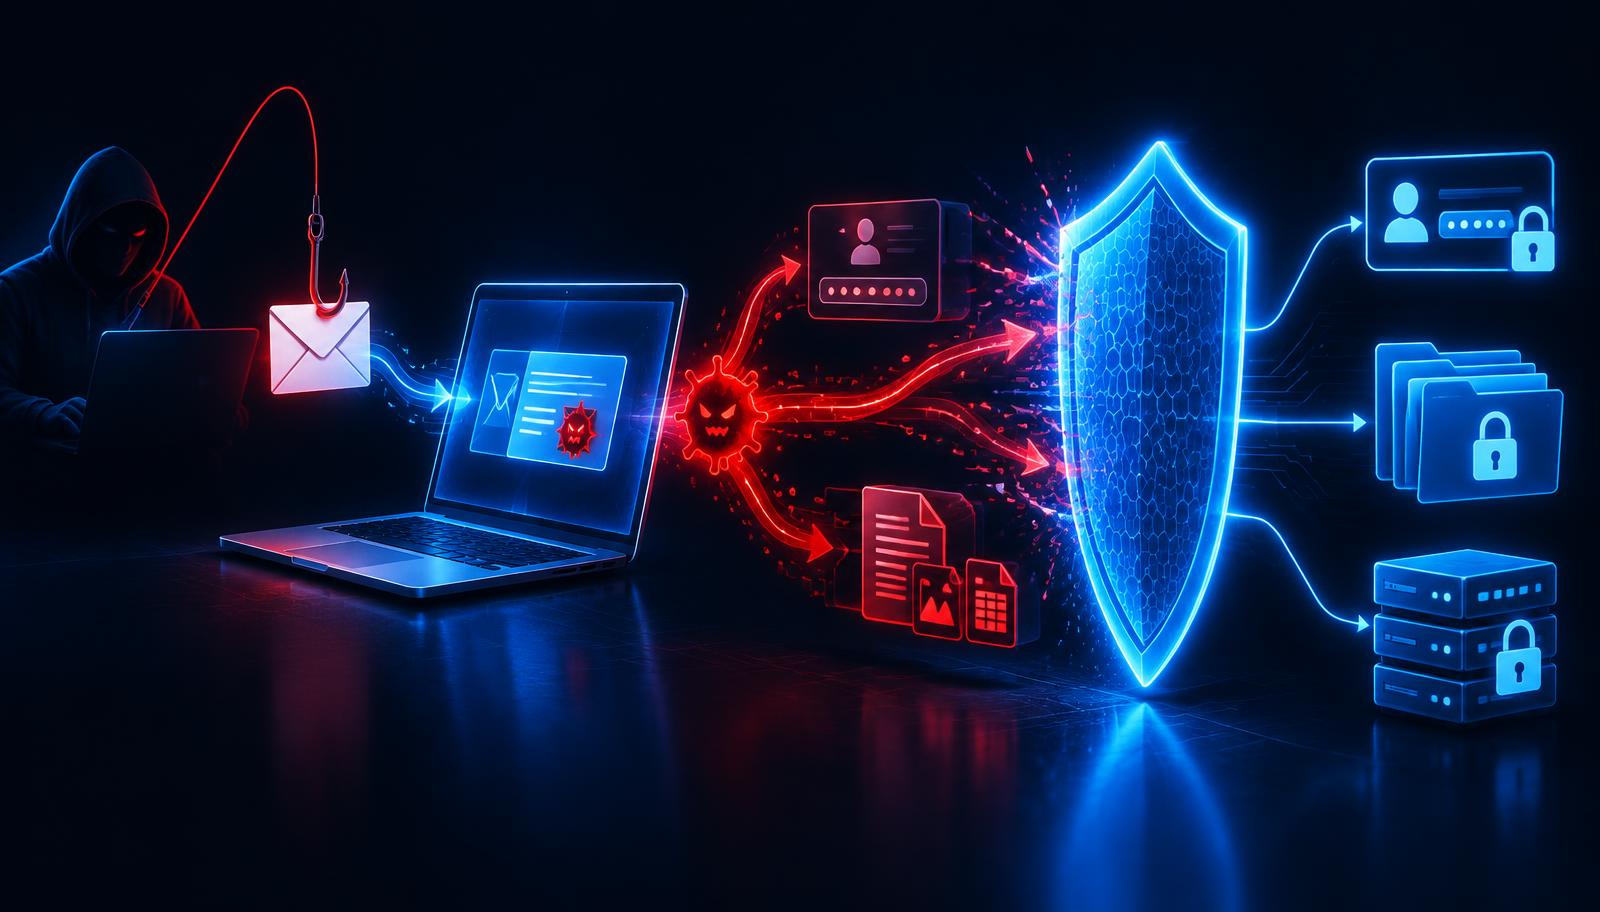
Attack chain
How one deceptive message becomes an incident
Breaking any link in the chain can stop the attacker.
Lure
Urgent or trusted-looking message
Interaction
Link, attachment or reply
Execution
Credential theft or malicious code
Access
Account or device compromise
Impact
Fraud, data theft or disruption
Phishing, malware and social engineering explained with real examples
Three techniques cause the overwhelming majority of cyber crime in India: phishing, malware and social engineering. They often work together. Once you can recognise them, you are harder to fool than most people — and you will answer interview questions about them better too.
reviewed | 2026-10-13 | Original Verizon 2025 DBIR executive summary and human-element analysis checked. Global dataset denominator retained; these figures are not India-only or hiring statistics.01Lure
A message impersonates a trusted sender | user
02Interaction
A link, attachment or request creates the opportunity | network
03Compromise
Credentials are stolen or malicious code executes | lock
04Access
The attacker uses the account or device | laptop
05Impact
Fraud, data loss or operational disruption follows | database
Phishing: the fake message that wants your secrets
What it is: a message pretending to be someone you trust — your bank, a courier, a government department, your boss — designed to make you click a link, open an attachment, or hand over credentials.
Real Indian examples:
- An SMS: "Your SBI account will be blocked. Update KYC immediately: sbi-kyc-verify.in" — the link leads to a perfect copy of the bank's site that steals your login.
- A WhatsApp message about an electricity bill: "Your power will be cut tonight, call this number" — the "officer" then walks you into installing a screen-sharing app.
- A fake delivery SMS with a "redelivery fee" page that captures your card details.
How to spot it: urgency and threats, a sender address that is almost-but-not-quite right, links that do not match the real domain, and any request for OTPs, PINs or passwords.
Malware: software that works against you
What it is: any program designed to harm or spy — viruses, spyware, ransomware, trojans.
How it reaches Indian users most often:
- Fake apps — "KYC update" or "customer care" apps sent over WhatsApp, or APK files from websites. Once installed, they read your SMS (including OTPs) and screen.
- Attachments — invoices or "resumes" that install malware when opened.
- Ransomware — locks your files and demands payment. This is what hits hospitals and companies in the news.
How to protect yourself: install apps only from official stores, keep your phone updated, never install apps a stranger asks you to, and keep backups of important files.
Social engineering: hacking the human, not the machine
What it is: manipulating people into breaking security rules. It is the technique behind almost every successful scam, because tricking a person is easier than defeating encryption.
Classic patterns:
- Pretexting — the caller invents a believable role: bank officer, police, IT support, even a colleague.
- Authority and fear — "This is the cyber crime branch, your Aadhaar is linked to a crime" (the infamous "digital arrest" scam). Real police never demand money or conduct arrests over video calls.
- Urgency — every social engineer manufactures time pressure so you act before you think.
The defence is a habit, not a tool: whenever someone creates urgency and asks for money, OTPs or app installs — stop, hang up, and verify through an official channel you found yourself.
How the three work together
A typical attack chain: a phishing SMS (phishing) convinces you to install a "bank verification" app (malware), and when you hesitate, a polished caller pressures you (social engineering). Breaking any single link stops the whole attack.
If you are targeted or scammed
- Call your bank immediately to freeze cards and accounts.
- Report at cybercrime.gov.in or call 1930 — fast reporting genuinely improves recovery chances.
- Change passwords on any account that shared the compromised password.
- Warn your family — scammers often target relatives next.
Why interviewers love these topics
If you are preparing for a security role, expect questions like "how would you investigate a phishing email?" or "how would you explain social engineering to a non-technical employee?" Our cyber security interview questions guide has model answers, and the free AI mock interview lets you practice saying them out loud. For everyday protection, see our 10 cyber security tips for India.
Frequently asked questions
What is phishing in cyber security? Fake messages that imitate trusted organisations to steal passwords, OTPs or money — the most common attack in India.
What is malware in cyber security? Any software designed to harm, spy or extort — including viruses, spyware, trojans and ransomware.
What is social engineering in cyber security? Manipulating people into revealing information or breaking security rules — exploiting trust and urgency instead of technical weaknesses.
Which is more dangerous: technical hacking or social engineering? Social engineering, by far. Most real breaches start with a fooled human, not broken code.
SOC evidence map
Identity | Failed and successful authentication; privilege; expected source | identity
Endpoint | Process ancestry; persistence; device context | laptop
Network | DNS and connections; source and destination; time window | network
SIEM | Rule logic; related alerts; visibility gaps | database
Response | Proportionate containment; escalation; preserve evidence | shield
Handover | Timeline; facts versus assumptions; next action | user